
 Nguyễn Chính Ngọc Liên
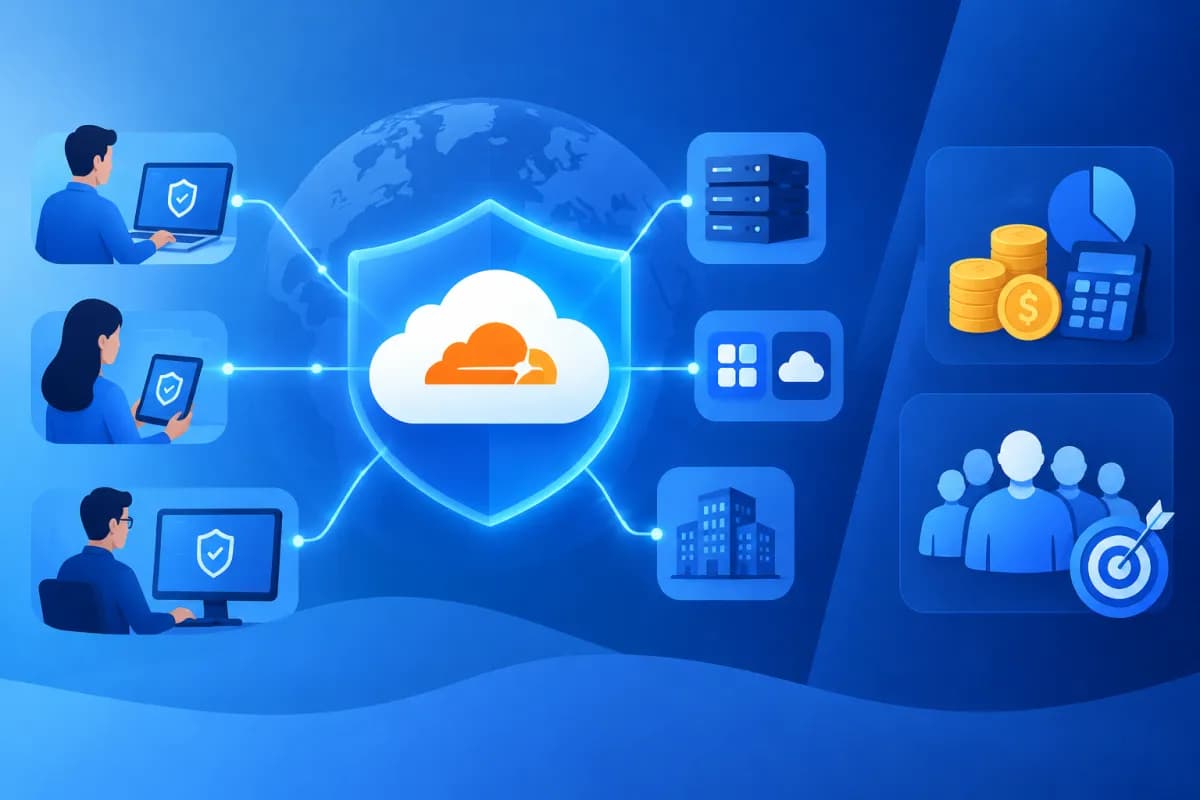
When employees work from multiple locations, applications move to the cloud, and business data becomes increasingly distributed, protecting the network with only an office firewall may no longer be enough. Businesses need to control users, devices, and access to individual applications.
What is Cloudflare Zero Trust, how is its cost calculated, and is it right for your business? This article explains its main components, the factors that affect your budget, and the situations in which it may be worth considering.
What Is Cloudflare Zero Trust?
Cloudflare Zero Trust is a group of security services that helps businesses control access to applications, the internet, and network resources according to the principle of never trusting by default. Rather than giving users broad access to the internal network once they connect to a VPN, the Zero Trust model verifies identity, device, and policy before granting access to each required resource.
This principle is often summed up as “never trust, always verify.” Users may need to sign in through a multifactor authentication system; devices may also have to meet requirements, such as being managed, running an up-to-date operating system, or having security software installed. Access is then granted based on role, user group, and application.
Cloudflare Zero Trust is not a single product that replaces every security tool. It is a platform made up of services that can work together according to an organization’s needs. Commonly discussed components include:
- Cloudflare Access: Controls access to internal applications, such as admin portals, HR systems, or developer environments. Users are authenticated before entering an application, rather than being given broader access to the entire network.
- Cloudflare Gateway: Helps apply policies to internet and network traffic, such as blocking risky domains or content, monitoring activity, and reducing the risk of visiting malicious sites by mistake.
- Cloudflare WARP: An application installed on users’ devices that supports connections to Zero Trust services and the enforcement of access policies. WARP should not be understood simply as a consumer VPN; its configuration and purpose depend on the deployment architecture.
- Advanced features: Depending on the plan and configuration, businesses may consider device posture checks, data controls, browser protection, or integrations with identity and device management systems.
The key point is that Zero Trust does not mean installing an application and becoming secure immediately. Its effectiveness depends on how policies are designed, identities are managed, applications are classified, and processes are handled when a user or device does not meet requirements.
How Is Cloudflare Zero Trust Priced?
There is no single fixed cost that suits every business. The actual price depends on the current service plan, number of users, required features, and deployment approach. Cloudflare may offer a free option as well as paid tiers for different needs, but feature coverage, limits, and terms can change over time, by region, or under an enterprise agreement. Check the official pricing and terms when preparing your budget.
When estimating costs, businesses should consider the following factors:
- Number of users: Some plans are priced by user or by the number of users with access. Include full-time employees, temporary staff, contractors, and partners who need to access your systems.
- Features to be deployed: Protecting internal applications alone has a different scope from combining access controls, traffic filtering, device checks, data protection, or advanced security features. Avoid buying a larger plan than you need before defining your goals.
- Environment size and complexity: The number of applications, locations, user groups, identity systems, and devices to manage affects configuration effort. Integrating with existing infrastructure may require additional technical resources, even if licensing fees do not increase proportionally.
- Support and operational requirements: Organizations that need in-depth support, service commitments, or a tailored deployment process should verify the relevant terms in the service plan and contract. Consulting, configuration, testing, and training costs should also be included in the total budget.
- How usage may grow over time: The number of employees and services may increase after deployment. Plan for user growth, expanded features, and logging and reporting needs so you do not account only for the initial cost.
For a fair budget comparison, separate subscription costs from deployment and operational costs. An option with low software fees may still require significant time to design policies, handle exceptions, and support users. Conversely, a thorough initial investment may reduce the risk of granting overly broad access or disrupting work later.
Before choosing a plan, list your users, the applications to protect, device groups, and security requirements. This gives you a basis for defining the right scope instead of relying on a generic estimate.
Which Businesses Should Consider Cloudflare Zero Trust?
Cloudflare Zero Trust may suit organizations that want more granular access management, especially when employees work remotely or applications no longer sit entirely within the office network. Situations worth considering include:
- Businesses with flexible work arrangements: Employees working from home, traveling for business, or working across multiple offices need consistent access to internal applications, rather than relying entirely on network location.
- Companies using multiple SaaS applications and internal systems: They need a centralized way to verify identity, assign permissions by group, and prevent accounts from accessing unrelated resources.
- Organizations working with external contractors or partners: They can grant limited access to only the required application or environment, then revoke it when a project ends.
- Businesses looking to reduce reliance on traditional VPNs: If the current VPN gives users overly broad network access or is difficult to manage, application-level access may be an approach to evaluate. Any replacement should be tested against actual systems and workflows.
- Organizations focused on control and auditability: IT or information security teams need to apply consistent policies, monitor access activity, and improve their ability to detect unusual behavior.
Small businesses can also consider the solution, but should not adopt it just because it is a trend. If they have only a few simple applications, few users, and no specific security requirements, they should weigh the benefits against the administrative effort and total cost. Larger companies or organizations in industries with stringent data protection requirements should carefully assess whether the solution meets their policies, regulatory obligations, and audit processes.
How to Assess Whether It’s a Good Fit Before Deployment
To avoid overly complex configurations or disruption, businesses should start by identifying the problem they need to solve. For example, employees may be sharing accounts, the VPN may grant broad access, admin applications may be publicly exposed, or contractor access may be difficult to revoke. Each problem should be tied to a measurable objective.
1. Review Users, Applications, and Devices
List who needs access to which systems, from which devices, and under what circumstances. Classify applications by sensitivity and identify the identity system in use. If user data or access permissions are not up to date, address this foundational work before or alongside the project.
2. Design Policies Based on Risk
Not every application needs the same policy. You could require multifactor authentication for sensitive systems, limit permissions by job group, and require compliant devices for access to important data. Policies should be robust without creating unnecessary barriers for employees.
3. Test with Different Groups
Run a pilot with a group of users and a representative set of applications before rolling it out across the company. During this phase, monitor login errors, latency, false blocks, and the volume of support requests. Pilot results can help refine policies and improve the accuracy of your cost estimate.
4. Account for Ongoing Operations
Determine who will manage policies, how users will be added or removed, how compromised devices will be handled, and how access rights will be reviewed periodically. A security platform delivers value only when it is kept up to date as the business’s workforce, applications, and risks change.
Conclusion
Cloudflare Zero Trust is a group of services that helps businesses control access based on identity, devices, and policies, instead of automatically trusting every connection on the internal network. Its cost depends on the number of users, features, environment complexity, and deployment resources. It is worth considering for organizations with flexible workforces, multiple applications, or a need to restrict access more closely, but the decision should be based on real business requirements.
If your business needs to review its digital infrastructure, security processes, or system integrations, LilyTech can help you assess your needs and develop an approach suited to your operational goals. Contact LilyTech to discuss your requirements, deployment scope, and budget plan before choosing a solution.

