
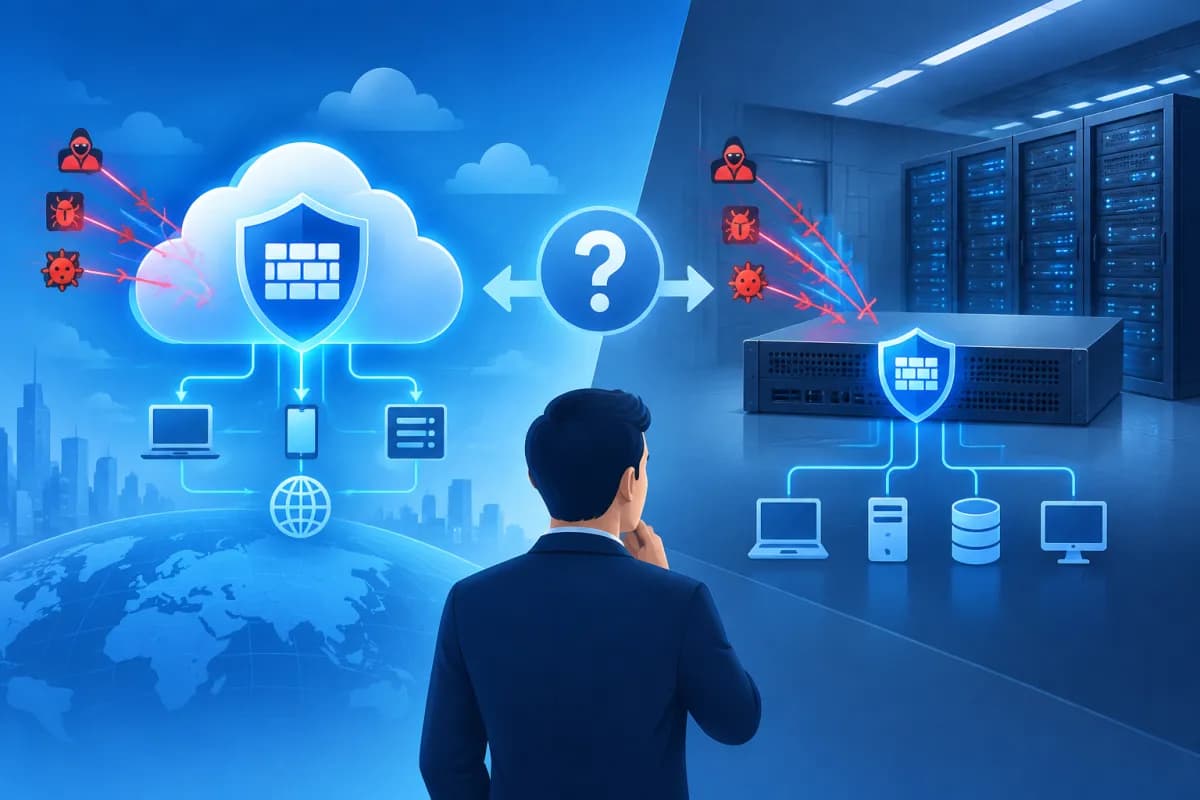
A WAF (Web Application Firewall) monitors and filters traffic to websites and applications. It can detect and block threats such as SQL injection, cross-site scripting (XSS), malicious bots, and certain types of application vulnerability exploits. When weighing cloud WAF vs on-premises WAF, it helps to understand how each approach works and what your business needs.
The two common models are cloud WAF and on-premises WAF. Each has its own deployment approach, cost structure, and operational requirements. Choosing the right option involves more than comparing security capabilities: you also need to consider your business’s size, existing infrastructure, team expertise, and compliance requirements.
What are cloud WAF and on-premises WAF?
Cloud WAF
A cloud WAF is a web application protection service delivered through a cloud platform. Traffic typically passes through the provider’s system before reaching your business’s servers. The WAF analyzes requests, applies security rules, and allows or blocks access according to its configuration.
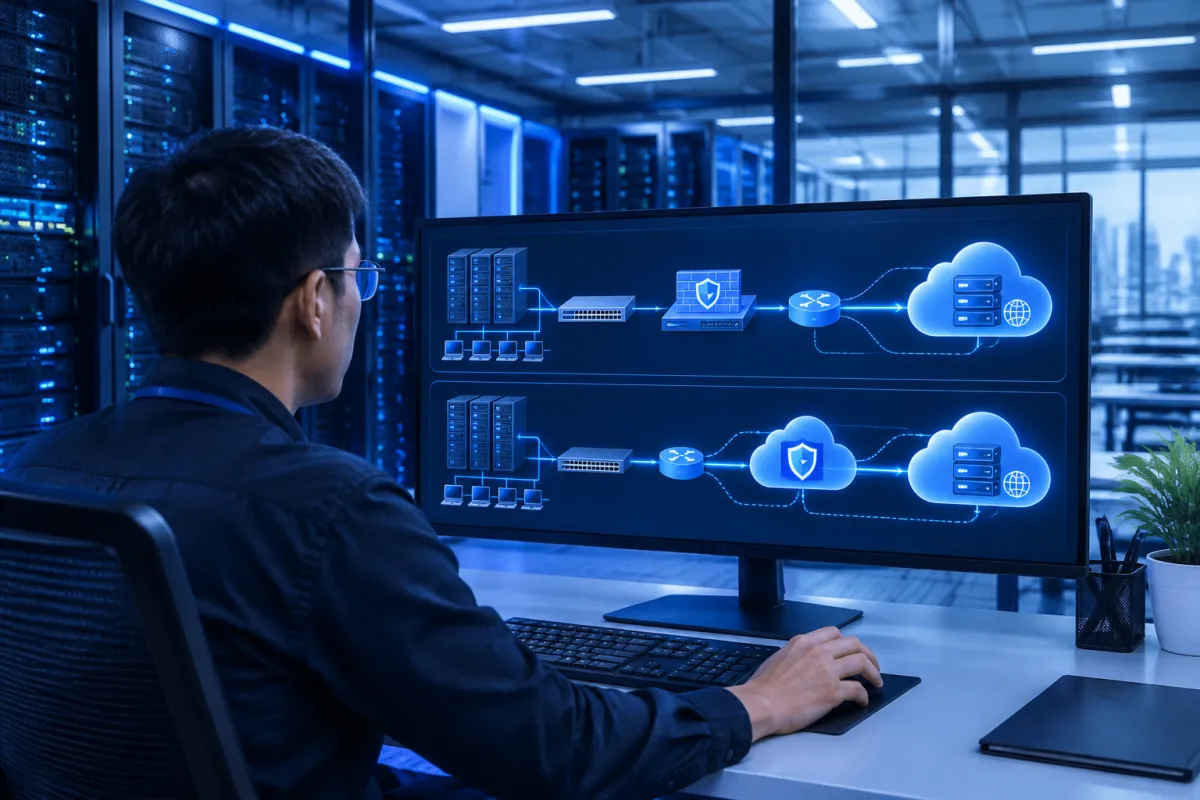
Businesses typically manage the service through an online dashboard or API. The provider is responsible for operating the platform, maintaining the infrastructure, and updating many of its protection rules. Depending on the service, a cloud WAF may be offered on its own or bundled with a CDN, DDoS protection, and other security tools.
On-premises WAF
An on-premises WAF is installed and operated in a data center or infrastructure environment controlled by the business. It may run on a dedicated appliance, a virtual server, or software deployed on site. The business manages its configuration, updates, and integration with application systems.
This model offers greater control over infrastructure and data, but requires a technically capable team. The business must monitor alerts, respond to incidents, assess performance, and plan upgrades.
Comparing the advantages and disadvantages of the two models
No WAF model is best for every situation. The key differences lie in the level of control, deployment speed, and how much work the business must handle itself.
- Deployment: A cloud WAF can usually be activated quickly, without purchasing and installing equipment on site. An on-premises WAF requires architecture planning, installation, and testing before it can go live.
- Scalability: A cloud WAF is often easier to scale when traffic increases or a business expands its services, subject to plan limits and provider capacity. With an on-premises WAF, the business must forecast resource needs and add infrastructure as demand grows.
- Control: An on-premises WAF gives the business direct control over configuration, deployment location, and data flows. A cloud WAF reduces infrastructure overhead, but some operational responsibilities depend on the provider.
- Operations: With a cloud WAF, the provider manages the platform, while the business still needs to monitor policies and alerts. With an on-premises WAF, the internal team takes on more responsibility, from updates to incident response.
- Connectivity requirements: A cloud WAF usually requires changes to routing or DNS to send traffic through the service. An on-premises WAF may suit environments where internal traffic flows need close control, but its network configuration must also be designed carefully.
A cloud WAF does not mean security is handled entirely automatically. If rules are too permissive, some malicious requests may get through; if they are too strict, legitimate users may be blocked. Likewise, an on-premises WAF is only effective when it is updated and monitored regularly.
WAF costs: more than just the license price
When comparing the costs of cloud WAF vs on-premises WAF, businesses should assess total cost of ownership (TCO) rather than focusing only on service fees or the upfront price of equipment. The actual cost includes implementation, staffing, maintenance, and the impact on business operations.
Cloud WAF costs
Cloud WAF services typically use a subscription model or charge based on factors such as traffic, request volume, features, and support level. Businesses do not need to invest in dedicated equipment upfront, so this option may suit a limited implementation budget or a need to get a solution up and running quickly.
However, recurring costs may rise with traffic or when the business adds advanced features. Check how pricing works during traffic spikes, the terms of service, and technical support fees to avoid unexpected costs.
On-premises WAF costs
An on-premises WAF may involve upfront costs for equipment or licenses, integration design, and testing. Businesses also need to account for staffing, maintenance, updates, equipment replacement, and capacity expansion as traffic grows.
For organizations with existing infrastructure and an experienced team, long-term costs may be easier to forecast in some cases. But if additional in-house capabilities need to be built, total costs may exceed the amount shown in the initial quote.
Compare WAF options by total cost of ownership over the expected period, and factor in the cost of security incidents, service disruptions, and the time your team will spend on operations.
Operational capabilities and security requirements
WAF effectiveness depends heavily on how it is deployed and operated. Before choosing a model, businesses should determine who is responsible for managing policies, handling alerts, and coordinating incident response. Without clear ownership of these tasks, either a cloud WAF or an on-premises WAF can underperform.
A cloud WAF may suit businesses looking to reduce infrastructure management or those without a dedicated security team. The service can help deploy common protection layers quickly, but businesses still need to review logs, fine-tune rules to match application behavior, and verify how the provider handles data.
An on-premises WAF may be a better fit when a business needs direct control over its deployment environment, requires deep integration, or already has a team capable of operating it. In return, the responsible team must track versions, update signatures and rules, check capacity, and rehearse incident response procedures.
For either model, assess log collection and export capabilities, data retention periods, incident support procedures, service availability, and how failures are handled. Businesses should also check what happens if a connection or appliance goes down, ensuring an appropriate balance between security and website availability.
How to choose the right WAF for your business
To decide between cloud WAF vs on-premises WAF, businesses can evaluate the following criteria:
- Define protection requirements: List the websites, applications, and APIs that need protection; the types of data they handle; and relevant risks and compliance requirements. Different applications may need different WAF policies.
- Assess your infrastructure: Determine whether your systems are on site, in the cloud, or spread across multiple environments. Check traffic routing capabilities, latency requirements, and failover options.
- Take stock of your resources: Assess your team’s experience in configuration, monitoring, and incident response. If you lack specialized staff, factor in support services or a suitable managed model.
- Build a TCO budget: Compare recurring service fees with equipment, licensing, staffing, maintenance, and expansion costs over the same period.
- Test before a broad rollout: Run the WAF in monitoring mode or test it on a representative application. Assess detection capabilities, false-positive rates, latency, and ease of operation.
- Review the service agreement: Clarify the scope of support, availability commitments, incident notification procedures, data access rights, and options for switching providers.
A cloud WAF is often worth considering when you need fast deployment, want to limit on-site infrastructure investment, and can use an external service under your business policies. An on-premises WAF is often a better fit when an organization needs deep control, has in-house technical expertise, and wants to manage the platform itself. Some businesses may also use a hybrid model to meet different requirements across their applications.
Conclusion
Both cloud WAF and on-premises WAF can help protect websites, but they differ in control, cost, and operational workload. Choose based on your security requirements, infrastructure architecture, team capabilities, and total cost of ownership. After deployment, test the solution, monitor it, and regularly fine-tune its policies.
If your business is considering website protection or needs an infrastructure assessment before deploying a WAF, contact LilyTech for advice on an approach that fits your goals, budget, and operational capabilities.

