
 Nguyễn Chính Ngọc Liên
Card payments make it easier for businesses to serve customers, but they also carry a responsibility to protect payment data. A leak of card numbers, verification codes, or cardholder information can cause financial losses, damage a company’s reputation, and disrupt business operations. That’s why preparing for PCI DSS compliance for businesses should be treated as part of risk management, not just a procedure for the IT department.
This article outlines a practical path for businesses to define their scope, assess their current state, address gaps, and maintain PCI DSS compliance. The specific approach depends on the payment model, business size, and requirements set by the acquiring bank or relevant partners.
What is PCI DSS, and which businesses should care?
PCI DSS (Payment Card Industry Data Security Standard) is a security standard for the payment card industry, designed to protect cardholder data and payment processing environments. It applies to organizations that store, process, or transmit card data, and may also apply to service providers that can affect the security of these environments.
Businesses don’t have to operate a bank to fall within PCI DSS scope. Examples include retailers that accept card payments in stores, e-commerce platforms that take online payments, businesses that store card details for recurring payments, and service providers that process transactions. Using a third-party payment gateway may reduce the scope of systems that need to be assessed, but it does not automatically eliminate all of a business’s responsibilities.
PCI DSS is organized around 12 control requirements covering topics such as network protection, cardholder data security, vulnerability management, access control, system monitoring, and maintaining security policies. Businesses should confirm the applicable version and compliance validation method with their acquiring bank, service provider, or relevant authority. They should also distinguish between meeting the standard’s requirements and holding a general certification: assessment methods and validation documents may vary by an organization’s role and level.
Step 1: Define the scope and payment processing model
Before buying tools or deploying technical measures, businesses need to know what data is processed, where it flows, and who can access it. This is a foundational step: the less accurate the scope, the more likely an assessment is to miss relevant systems, personnel, or vendors.
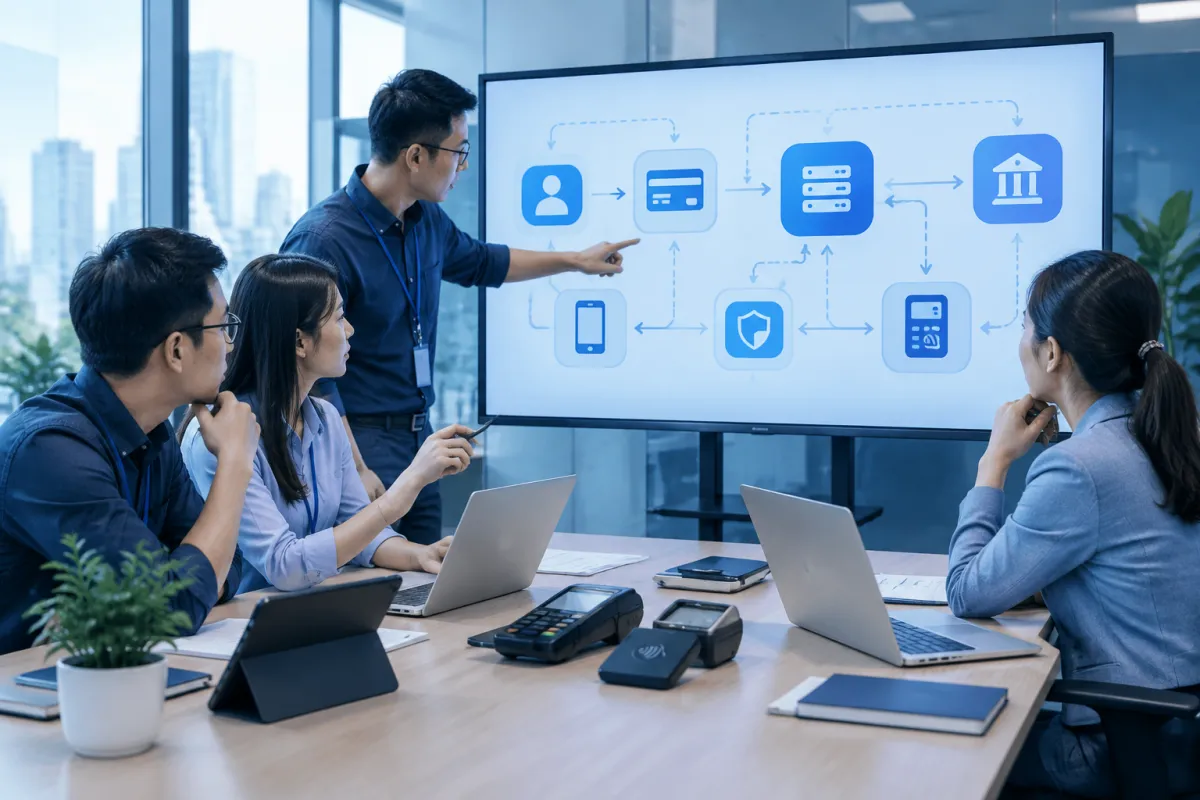
- List payment channels: websites, apps, in-store devices, call centers, recurring payments, and offline processing procedures.
- Map data flows: document where card data is collected, transmitted, processed, stored, and deleted; identify the systems connected to each point.
- Inventory assets: relevant servers, databases, endpoints, networks, administrator accounts, software, and development environments.
- Review third parties: payment gateways, hosting providers, technology service providers, and partners with access to or influence over the payment environment.
Businesses should minimize storing card data themselves unless they have a business need and the capacity to protect it. They can consider redirecting customers to a partner’s payment page or using an appropriate encryption or tokenization solution. These options may help narrow the scope, but an expert should assess them and confirm them with the party receiving the compliance report.
Step 2: Assess the current state and identify gaps
After defining the preliminary scope, compare the actual environment with the PCI DSS requirements that apply to the business model. Don’t rely on policy documents alone: check configurations, logs, operating procedures, and evidence that security measures are working.
A current-state assessment typically reviews the following:
- Network and configuration management: segment the payment environment from office or guest networks; manage firewalls, network devices, and configuration changes.
- Data protection: identify sensitive data, encrypt it in transit or at rest as required, control encryption keys, and define retention periods.
- Access management: assign role-based access according to the principle of least privilege; use strong authentication, manage privileged accounts, and revoke access when employees change roles or leave.
- Secure operations: patch vulnerabilities, conduct appropriate scans and tests, protect endpoints, monitor logs, and prepare incident response procedures.
- Governance: maintain security policies, train employees, manage vendors, and assign an owner to each control.
Document the findings in a gap list. For each issue, include its risk level, affected systems, owner, remediation deadline, and required evidence. If the business lacks the right in-house expertise, consult a QSA (Qualified Security Assessor) or another qualified specialist to clarify how requirements should be interpreted. Early consultation can help avoid misdirected investment.
Step 3: Create a remediation plan and strengthen controls
Use the gap list to build a prioritized plan rather than trying to do everything at once. Address issues that could expose data, overly broad access, or uncontrolled system connections first. The plan should also account for budget, acceptable downtime, and dependencies between tasks.
- Reduce data and narrow the scope: remove unnecessary data, establish secure deletion procedures, and isolate payment processing systems.
- Strengthen the security architecture: update network configurations, implement appropriate segmentation, encrypt data as required, and tightly manage encryption keys.
- Standardize identity and access management: use multifactor authentication where required, review access regularly, and keep records of access grants, changes, and revocations.
- Establish continuous operations: manage patches, scan for vulnerabilities, conduct security testing, centralize logs, and develop procedures to detect, report, and handle incidents.
- Complete documentation and training: issue policies and procedures, provide employee guidance, and require vendors to maintain relevant compliance evidence.
Every control should have an owner and verifiable evidence, such as approved configurations, access review records, scan results, monitoring logs, or training records. Test changes in an appropriate environment, document approvals, and verify the results after deployment. Technology does not replace governance responsibilities: scanning tools and firewalls are effective only when properly configured, monitored, and supported by timely alert handling.
Step 4: Validate compliance, maintain records, and sustain it
Once the main gaps have been addressed, conduct an assessment using the method appropriate to the business’s level and the requirements of its acquiring bank or partners. Depending on the situation, validation may include a Self-Assessment Questionnaire (SAQ), Report on Compliance (ROC), Attestation of Compliance (AOC), external vulnerability scans, or an assessment conducted by a QSA. Not every business needs the same set of documents, so confirm the applicable requirements before planning.
Before an assessment, check that the scope is up to date, every in-scope system has an owner, evidence is current, and previous findings have been addressed. If any requirement is unmet, agree on remediation measures, deadlines, and how the results will be rechecked. Avoid claiming compliance without supporting evidence or before completing the required validation process.
PCI DSS is not a one-time project. Businesses need to maintain security activities on an ongoing basis: review access rights, monitor alerts, manage changes, check vendors, update documentation, and train employees. Major changes—such as switching platforms, adding a payment method, expanding infrastructure, or changing providers—should be assessed for their impact on scope and compliance.
Conclusion: Start with the right scope and keep improving
To achieve PCI DSS compliance for businesses, follow a controlled roadmap: map data flows and define scope, assess the current state, prioritize gap remediation, prepare assessment evidence, and maintain controls regularly. This approach helps reduce security risks while limiting unnecessary costs from unfocused implementation.
Every business has a different payment model, infrastructure, and set of obligations. LilyTech can work with businesses to review systems, recommend technology solutions, and develop an implementation roadmap aligned with business goals. Contact LilyTech for advice on preparing for compliance and strengthening security across your payment operations.

