
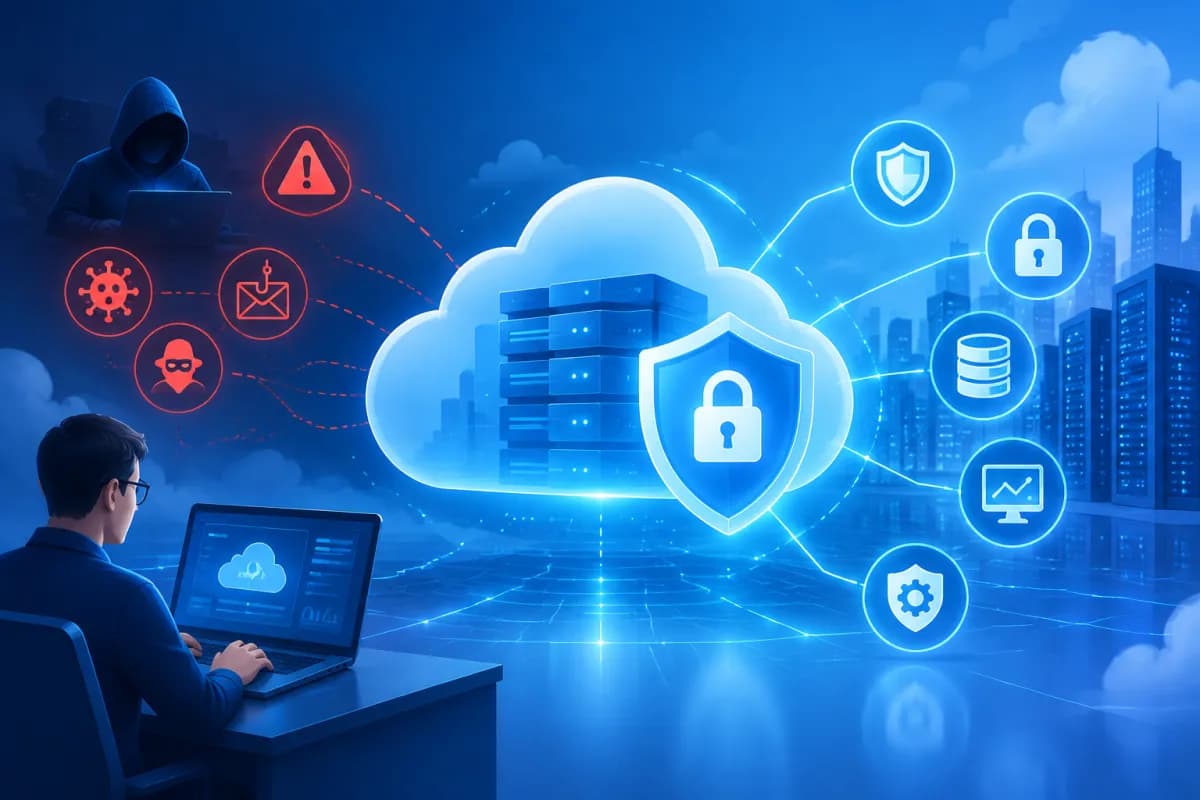
Cloud computing helps businesses store data, run applications and work flexibly without investing in an entire on-premises server infrastructure. However, moving data online also raises a common concern among business owners: Is cloud computing safe? Risks and solutions are important to understand—and what can you do to reduce the risk of data loss?
The answer depends on the provider, how the service is configured and the business’s management processes. Cloud platforms can be highly secure, but they do not automatically eliminate every risk. This article will help you identify common threats and put suitable safeguards in place.
Is cloud computing safe?
Cloud computing can be safe if a business chooses a trustworthy provider and proactively implements the necessary security measures. Major providers typically invest in data centers, system monitoring, encryption and incident response processes at a scale that many businesses would find difficult to build themselves. However, using a reputable provider does not mean your data is completely protected.
One important point to understand is that security responsibilities are usually shared between the provider and the customer. The provider is responsible for protecting the underlying infrastructure within the scope of the service; the business still needs to manage accounts and access permissions, configure storage, protect endpoint devices and control how employees use data. The exact division of responsibility can vary across cloud infrastructure, platform and software services.
So, the right question is not only “Is the cloud safe?” but also “Does this service model meet the business’s needs, and has it been configured correctly?” Effective security requires a combination of technology, processes and people—not complete reliance on a single provider.
Common security risks when using cloud computing
Data leaks caused by misconfiguration
Inappropriate storage settings or sharing permissions can make internal data more widely accessible than intended. For example, a shared folder might be set to public, a service account might have excessive permissions, or a test environment containing real data might not be adequately protected. This risk deserves attention because it does not necessarily result from a sophisticated attack; sometimes, a single overlooked setting is all it takes.
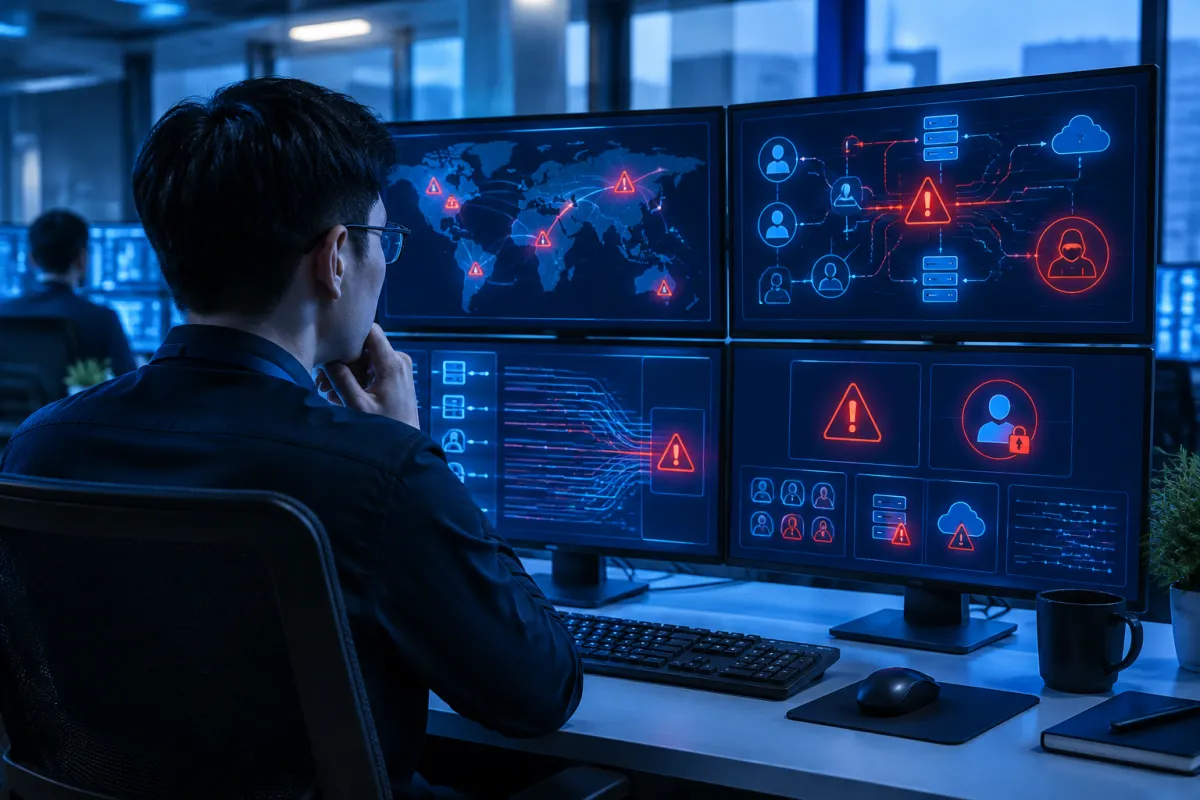
Account takeover
Attackers may steal passwords through phishing emails, use credentials exposed in a breach of another service or exploit accounts that are no longer managed. If an account has broad access, the consequences could include downloading data, changing settings, deleting backups or creating unauthorized accounts. Administrator and shared accounts require particularly close control.
Data loss and service disruption
Data may be accidentally deleted or overwritten, encrypted by malware, or become inaccessible because of technical failures, connectivity disruptions or integration errors. Recovery capabilities depend on backup policies, retention periods and restoration processes. Synchronizing data across devices is not always a substitute for an independent backup: deletions or encryption can also be synchronized to other copies.
Malware, vulnerabilities and third-party risks
Applications connected to cloud platforms may have vulnerabilities, use outdated libraries or request more access than they need. Software providers, integration partners and external staff can also become weak links if their accounts or processes are not controlled. In addition, malware on an employee’s device can expose login credentials and business data.
Compliance risks and lack of transparency
Businesses need to know how and under what conditions data is stored, processed and backed up, who can access it, and how the provider will notify them of an incident. Failing to review contracts, retention policies or relevant regulations can make it difficult to demonstrate that customer information is being protected. Specific requirements depend on the type of data and the industry.
Ways to protect data on cloud platforms
Choose the right provider and service
Before implementation, businesses should assess a provider’s security capabilities, service availability, backup options, recovery capabilities and incident response procedures. Carefully review terms covering data ownership, storage location, retention periods, technical support and data export when a contract ends. Certifications or security control documentation can support your assessment, but make sure they apply to the specific service and how you plan to use it.
Use strong authentication and the principle of least privilege
Enable multi-factor authentication for administrator accounts and accounts with access to sensitive data. Each employee should have an individual account; limit shared accounts so actions can be traced. Grant only the permissions needed for each person’s work, review access regularly and revoke it as soon as an employee changes roles or leaves. Administrator accounts should be separate from everyday work accounts, and important changes should be logged.
Encrypt, back up and test recovery
Encrypting data in transit and at rest can reduce the impact of unauthorized access, but businesses need to understand how encryption keys are managed and what each party is responsible for. Set up backups according to the importance of the data, store copies in a separate environment and restrict who can delete them. Most importantly, test recovery regularly to confirm that the data is usable and restoration times meet operational needs.
Monitor, update and prepare for incidents
Enable activity logs and alerts for suspicious behavior, such as unusual logins, permission changes, large-volume data downloads or disabled security controls. Update operating systems, applications and integrated components on a schedule, and remove services that are no longer in use. Businesses should also have an incident response plan that identifies who is responsible, how to isolate a compromised account, which communication channels to use and how to restore operations.
A secure implementation process for businesses
To avoid making decisions by guesswork, businesses can start by creating an inventory of their data and classifying it by sensitivity. Customer information, financial data, personnel records and internal documents may require different levels of protection. From there, identify who needs access, where the data is stored and which systems exchange information.
- Assess risks: Identify critical assets, potential threats and their impact on business operations.
- Choose the right model: Consider public, private or hybrid cloud services based on security requirements, budget and operational capabilities.
- Set up controls: Configure permissions, multi-factor authentication, encryption, logging and backup policies before moving important data to the system.
- Test and train: Run recovery drills and teach employees how to recognize phishing emails and report incidents.
- Review regularly: Check access permissions, configurations, contracts and whether the service still meets the business’s needs as they change.
Small businesses do not need to implement a complex suite of solutions from day one. They can prioritize foundational measures such as multi-factor authentication, appropriate access permissions, independent backups and employee guidance. As data volumes or compliance requirements grow, add more advanced monitoring and suitable management processes.
Conclusion: Cloud security is a shared responsibility
Cloud computing can be a safe and effective choice when a business understands its responsibilities, chooses the right provider and maintains safeguards throughout its use of the service. Risks often stem from misconfigurations, weak accounts, insufficient backups or unclear processes. These can be reduced through careful management and regular checks.
If your business is considering digital transformation, building a website or application, or integrating data with an ERP system, define your security requirements at the design stage. LilyTech can help you choose technology solutions that fit your business goals and resources. Contact LilyTech to discuss your needs and build a practical, secure implementation roadmap.

