
 Nguyễn Chính Ngọc Liên
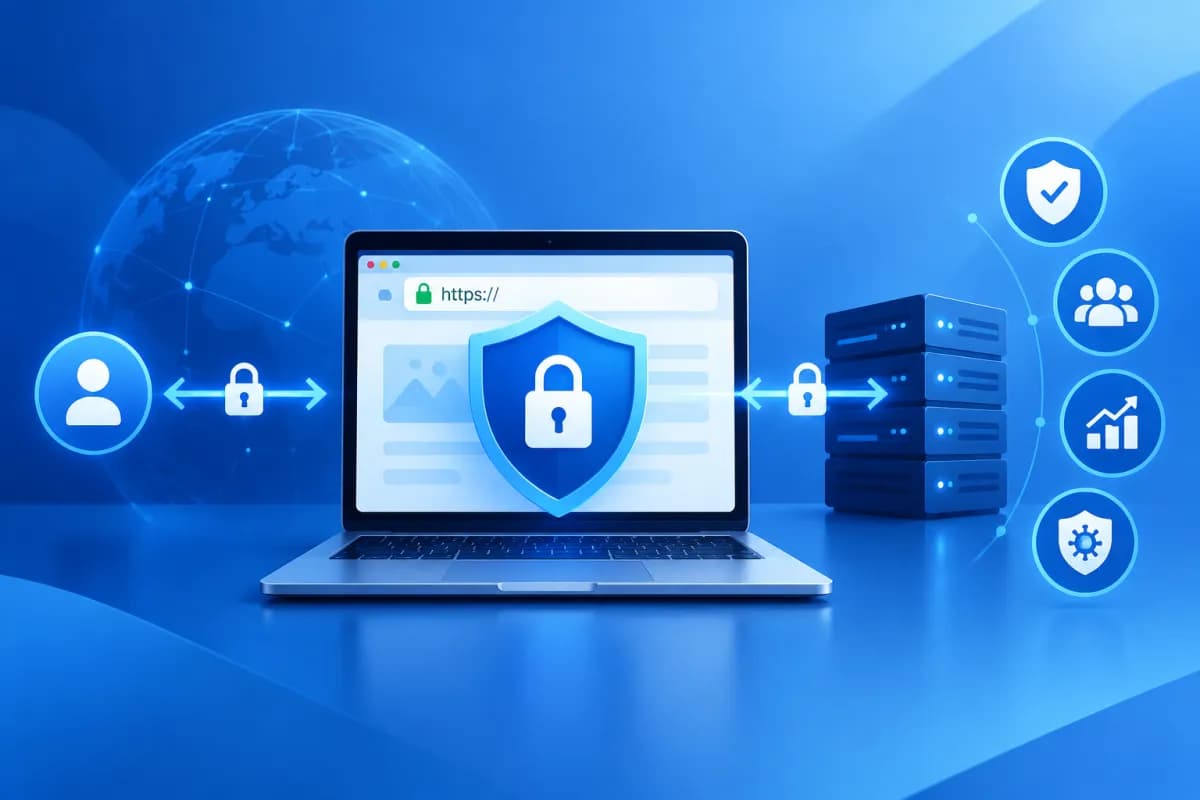
When you visit a website, you may notice its address begins with “https://” and a padlock appears in the browser bar. These are common signs of an SSL/TLS certificate, an important technology that protects data exchanged between a website and its users. For businesses, SSL is about more than information security—it also shapes how customers perceive the brand.
So, what is SSL, how does the certificate work, and does your website need one? This article explains the basic concepts, benefits, how to choose a certificate, and what to consider during implementation so you can make an informed decision.
What Is SSL?
SSL stands for Secure Sockets Layer, a protocol developed to protect data transmitted over a network. It creates a secure connection between a user’s browser and a website’s server, encrypting data as it travels. This makes it difficult for unauthorized parties to read or exploit information if they intercept it in transit.
The original SSL protocol is now obsolete and has been replaced by TLS, which stands for Transport Layer Security. However, in everyday conversation, “SSL” is still widely used to refer to SSL/TLS certificates and HTTPS connections. So when a provider says a website needs to buy or install SSL, they usually mean a certificate that enables a secure TLS connection.
An SSL/TLS certificate is a data file installed on a server. It verifies a website’s identity to a certain extent and helps establish an encrypted connection. When configured correctly, the certificate allows users to access the website via HTTPS rather than HTTP. HTTPS is HTTP transmitted over a secure TLS connection.
How Do SSL/TLS Certificates Work?
A secure connection is established automatically in a few steps. Users don’t need to do anything technical; the browser and server exchange information to verify the certificate and agree on an appropriate encryption method.
- The browser connects to the website: When a user enters an HTTPS address, the browser sends a request to the website’s server to start a secure session.
- The server sends its certificate: The server provides an SSL/TLS certificate containing information such as the domain name, expiration date, and certificate issuer.
- The browser verifies the certificate: The browser checks whether the certificate is valid, matches the domain name, and was signed by a trusted issuing authority. If there is a problem, the browser may display a warning.
- Both parties establish a session key: After verification, the browser and server use cryptographic methods to agree on a session key for that connection.
- Data is transmitted in encrypted form: Subsequent exchanges are encrypted with the session key. Only parties in the connection with the appropriate key can decrypt the data.
In practice, this process combines several cryptographic techniques. Public-key cryptography helps verify identities and establish the connection, while symmetric encryption is generally used to protect data during the session because it is more efficient. The website’s server must be managed and TLS configured correctly; the browser handles most of the verification and connection process.
It’s important to remember that encryption protects data only while it travels between the browser and server. SSL/TLS does not automatically prevent every type of attack, guarantee a website is free of malware, or confirm that all content on a website is trustworthy. Businesses still need to secure their servers, update software, control access, and protect stored data.
Benefits of SSL for Websites and Businesses
1. Protects Information in Transit
Websites with login forms, checkout pages, registration features, or contact forms collect data from users. An HTTPS connection helps reduce the risk of that data being intercepted or altered as it travels across a network, particularly when users are on public networks. It is a basic layer of protection when handling passwords, personal information, or transaction data.
2. Helps Verify a Website’s Identity
A certificate allows the browser to check whether a website matches the identity information associated with it. This can reduce the risk of users being redirected to a fraudulent website in some types of attacks. However, the level of verification depends on the certificate type; a padlock does not mean the business has been fully vetted for legal compliance or business quality.
3. Helps Customers Feel More Secure
Browsers may warn users when a website does not use HTTPS or has a certificate error. Such warnings can make customers hesitate, especially when they are about to log in, submit information, or make a payment. By contrast, a correctly configured HTTPS connection provides a smoother browsing experience and shows that the business takes security seriously.
4. Provides a Foundation for Modern Website Features
Many browsers and web technologies require or favor HTTPS for features such as location access, some browser APIs, and progressive web apps. Using HTTPS can therefore improve a website’s compatibility with modern experiences while helping protect content from being tampered with in transit.
5. Supports SEO but Doesn’t Replace a Content Strategy
Google has announced that HTTPS is a lightweight ranking signal. This is a positive benefit, but installing SSL alone is unlikely to lead to a significant increase in search rankings. SEO still depends on many factors, including content quality, website structure, load speed, how well the site meets search intent, and its backlink profile. HTTPS should be considered an essential technical foundation, not a standalone SEO solution.
Common Types of SSL/TLS Certificates
Certificates are generally categorized by their level of validation or the scope of domains they cover. Businesses should choose based on their website structure, operational requirements, and verification process—not just price or marketing labels.
- DV (Domain Validation): Verifies control of the domain. This type is usually issued quickly and suits blogs, brochure websites, or small businesses that need basic HTTPS.
- OV (Organization Validation): In addition to verifying domain control, the issuer verifies certain details about the organization. This type may suit businesses that want an additional layer of organizational validation.
- EV (Extended Validation): Requires a more rigorous organization verification process. How browsers display EV information may vary by platform, so it should not be treated as a guarantee of higher rankings or sales.
- Wildcard: Can protect one primary domain and its first-level subdomains, depending on the certificate configuration—for example, subdomains for a blog or store. Check the coverage carefully before implementation.
- Multi-domain (SAN): Allows multiple domains or subdomains to be included in one certificate, which can be convenient for businesses managing several related websites.
Many websites can use free certificates from trusted issuers. A free certificate can still provide basic HTTPS encryption when issued and configured correctly. Paid certificates often include support services, organizational validation, or specific warranty terms. Businesses should review what is actually covered rather than assume that a more expensive certificate always provides stronger encryption.
How to Implement and Check SSL on a Website
To implement SSL/TLS effectively, businesses can work with their hosting provider, system administrator, or website design agency. The process usually involves the following steps:
- Assess requirements and domains: Determine whether the website uses one or multiple domains, which subdomains need protection, and whether the system has a separate testing environment.
- Choose the right certificate: Consider the validation level, domain coverage, validity period, automatic renewal options, and quality of technical support.
- Install the certificate on the server: Configure the certificate, certificate chain, and TLS protocol on the hosting service, dedicated server, or cloud platform running the website.
- Move the website to HTTPS: Update the configuration to redirect HTTP traffic to HTTPS. Check the admin area, forms, APIs, and any related subdomains.
- Fix mixed content: Replace resources such as images, scripts, and stylesheets that still load over HTTP with HTTPS versions. Otherwise, the browser may report that the page is not fully secure or block some resources.
- Update tracking tools: Check the website property in Google Search Console, the sitemap, and analytics settings to prevent interruptions to measurement data.
- Monitor renewals and alerts: Schedule certificate renewal or enable automatic renewal, then periodically check the expiration date, certificate errors, and redirects.
After installation, test important pages over HTTPS in multiple browsers and on different devices. Check the security indicator, data submission forms, login and checkout functions, and internal links. If the website uses multiple servers or a CDN, make sure the certificate is configured consistently across all content delivery points.
Conclusion: SSL Is an Essential Security Foundation
Understanding what is SSL helps businesses recognize the role of SSL/TLS certificates: they encrypt data in transit, help verify website identity, and contribute to a trustworthy user experience. HTTPS is also a suitable foundation for modern websites and can benefit SEO, but it cannot replace comprehensive security measures or a well-planned marketing strategy.
If your website doesn’t use HTTPS, displays a certificate warning, or needs a security configuration review, consult a technical provider before proceeding. LilyTech offers website design services and technology consulting tailored to business needs. Contact LilyTech for advice on building, operating, and growing a secure, effective website.

